Trust Center
Certified Security and Tested Governance Structures
ISO/IEC 27001
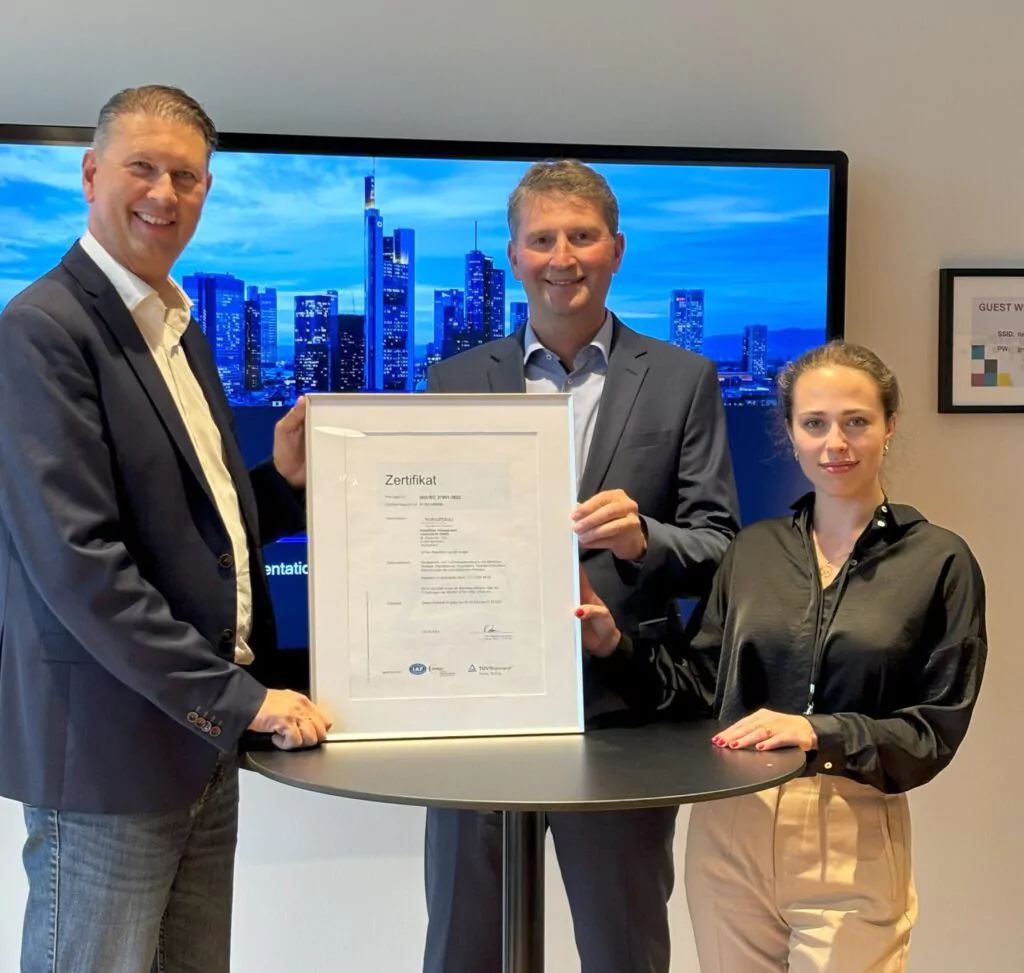
kobaltblau is certified under ISO/IEC 27001—the internationally recognized standard for information security management. This certification demonstrates that we operate a documented, effective, and continuously improved ISMS. Our certification is validated annually through external audits.
Continuous Security Management
Information security is not a project, but an ongoing process. Our Information Security Management System (ISMS) follows the PDCA cycle—we plan, implement, check, and continuously improve. Internal audits, regular management reviews, and external assessments ensure that our security standards are always state-of-the-art.
DSGVO / GDPR
We process personal data exclusively in accordance with the EU General Data Protection Regulation. Our privacy policy, internal guidelines, and technical and organizational measures are fully aligned with the requirements of the GDPR. An external data protection officer assists us in ensuring ongoing compliance with all data protection regulations.
No model training using your data
Input data and results from AI-powered processes are never used to train AI models—neither by kobaltblau nor by our infrastructure providers. Your data is used exclusively for the purpose for which it was entered.
Technical Safety & Infrastructure
Hosting exclusively within the EU
All systems and data are processed and stored on servers located within the European Union. We use Microsoft Azure and Amazon Web Services as our infrastructure providers in their respective EU regions. This ensures that your data remains subject to European data protection laws at all times.
Encryption at all levels
Data is consistently encrypted both during transmission and when stored. We use TLS 1.2 and TLS 1.3 for communication and AES-256 encryption for stored data—in accordance with the requirements of our ISO/IEC 27001 certification.
Minimal permission granting, maximum control
Access to systems and data is granted according to the least-privilege principle: Each person is granted only the permissions they need to perform their specific task. All access is logged and reviewed at regular intervals. Multi-factor authentication is required for privileged system access.
Early Detection and Rapid Response
Our systems are continuously monitored for anomalies and security events. In the event of a security incident, documented incident response processes—which are regularly tested and updated—are activated. Reportable incidents are communicated in a timely manner in accordance with GDPR requirements.

Our promise
We protect your data with the highest security standards and commit to the continuous improvement of our information security management system.